The Digital Front Door: Cybersecurity Essentials For Customer-Facing Platforms
For a service-based business, the website, client portal, scheduling system, payment page, and customer support tools often function as the digital front door. Customers may use these platforms to submit personal information, upload documents, make payments, or access account details. That makes security more than an IT concern. A compromised login or vulnerable third-party integration can interrupt operations and damage the trust a business has spent years building. Small and medium-sized companies need security controls that match the way customers actually interact with them.
Start With Identity, Not the Firewall
Many customer-facing systems are built around accounts. That makes identity one of the first areas to examine.
Multi-factor authentication should be available wherever sensitive customer or administrative information is accessible. Internal administrators deserve particular attention because a compromised privileged account can give an attacker significantly more access than an ordinary customer login.
Password policies should also account for modern attack methods. Businesses can block known compromised passwords, apply rate limits to repeated login attempts, and use protections against credential stuffing, where attackers test username and password combinations stolen from other services.
Authentication is only the first step. A system also needs to control what happens after someone logs in. Employees and customers should have access only to the information and functions required for their roles. An ordinary support employee, for example, may need to view a customer’s contact details without having permission to export the entire customer database.
Watch What Happens After a Successful Login
A valid username and password do not prove that the correct person is using an account. Attackers increasingly work with legitimate credentials, which means suspicious activity can occur after authentication.
Businesses should monitor for behavior that differs sharply from normal patterns. An account that suddenly downloads hundreds of files, changes contact information, adds a new payment method, or signs in from an unusual location may deserve additional verification.
The same principle appears in more advanced financial technology. Applications of AI in banking can include identifying patterns associated with suspicious transactions or account activity. A small service business does not need a bank-sized fraud operation to borrow the basic idea: look for behavior that does not fit the expected pattern and create a process for investigating it.
Automation can help surface unusual activity, but it should support rather than replace human judgment. A legitimate customer traveling internationally can look unusual to an automated system. Security controls need a way to distinguish suspicious activity from reasonable exceptions.
Protect the Information Customers Submit
Customer-facing platforms often collect more information than a business realizes. Contact forms may contain phone numbers and addresses. Appointment systems can store personal notes. Portals may contain contracts, invoices, tax documents, or other sensitive files.
Start by asking a simple question: Does the business need to collect each piece of information in the first place?
Data that is never collected cannot be exposed in a breach. If a form asks for information that employees never use, removing the field may reduce risk without affecting the customer experience.
Information that must be retained needs appropriate protection. Encryption should be considered for data moving between systems and for sensitive stored information. Access permissions should be reviewed regularly, especially when employees change roles or leave the company.
Retention policies matter as well. Keeping years of unnecessary customer information creates additional exposure without providing corresponding business value.
Treat Third Parties as Part of the Platform
A company’s website may look like one system to a customer while depending on numerous outside services behind the scenes. Payment processors, CRM platforms, analytics software, scheduling tools, live chat applications, cloud storage, and marketing platforms can all connect to customer-facing operations.
Every integration creates another relationship that needs attention.
Before connecting a new service, determine what information it can access, how authentication works, and what permissions the integration receives. An application that only needs customer email addresses should not receive broad administrative access simply because that is the easiest configuration.
Third-party access should also be reviewed after implementation. Old integrations are easy to forget, particularly when the employee who originally configured them leaves. An unused API key or abandoned plugin can remain an entry point long after its business purpose disappears.
Keep Customer Convenience From Weakening Security
Security controls can create friction, and poorly planned friction encourages workarounds. Customers who struggle to log in may repeatedly contact support, reuse simple passwords, or abandon the portal altogether.
The answer is not to remove meaningful protections. Instead, security and usability should be considered together.
Account recovery is a good example. A password reset process should make legitimate recovery reasonably straightforward without allowing an attacker to take control using easily discovered information. Sensitive account changes may warrant additional verification even after a user is logged in.
Error messages also require care. A login page does not need to tell an attacker whether a particular email address has an account. Small interface decisions can reveal useful information to someone testing the system.
Patch the Systems Customers Never See
A polished website can still rely on outdated software behind the scenes. Content management systems, plugins, server software, APIs, libraries, and other components need regular updates.
Businesses should maintain an inventory of the technology supporting customer-facing services. Without that inventory, it is difficult to know whether a newly disclosed vulnerability affects the company.
Updates should follow a defined process rather than depending on someone remembering to check. Critical vulnerabilities may require rapid action, while routine updates can move through scheduled testing and deployment.
Backups deserve similar discipline. A backup is valuable only if the company can restore from it. Periodic restoration tests can expose missing files, corrupted copies, or procedures that no longer work before an actual emergency occurs.
Prepare for the Incident Before It Happens
Even strong controls cannot guarantee that an incident will never occur. Preparation determines what happens next.
A practical incident response plan should identify who makes decisions, who investigates technical issues, how affected systems can be isolated, and how the company will continue essential customer operations. Contact information for outside IT providers, cybersecurity specialists, legal counsel, insurers, and other relevant parties should be readily available.
Logging is critical during this process. Authentication records, administrative changes, system events, and other relevant logs can help determine what happened and which accounts or information may have been affected.
Teams should also know how customer communications will be handled. Guessing publicly before the facts are established can create confusion. Silence without an internal process can be equally damaging.
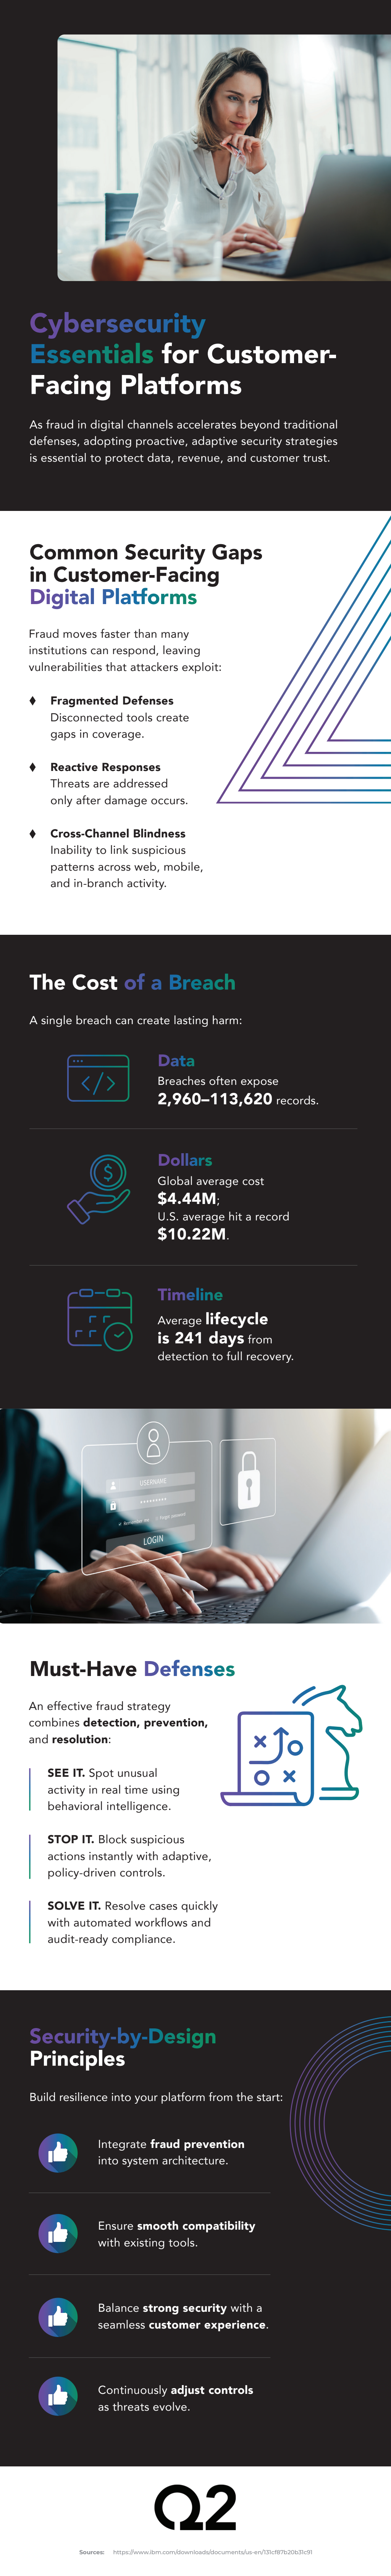
Cybersecurity for customer-facing platforms works best as a series of practical controls rather than a single security product. Strong authentication limits account compromise. Access controls reduce what compromised accounts can reach. Monitoring can reveal suspicious behavior, while patching, backups, and incident planning reduce the impact when something goes wrong. To learn more, look over the infographic below.